CodetoKloudCodetoKloudBook an AWS review

Hybrid On-Prem + Cloud Kubernetes over a WireGuard Mesh

A media company ran latency-sensitive streaming workloads on existing on-premise hardware and wanted cloud burst capacity, without dedicated links between sites. We joined both into one secure Kubernetes platform.

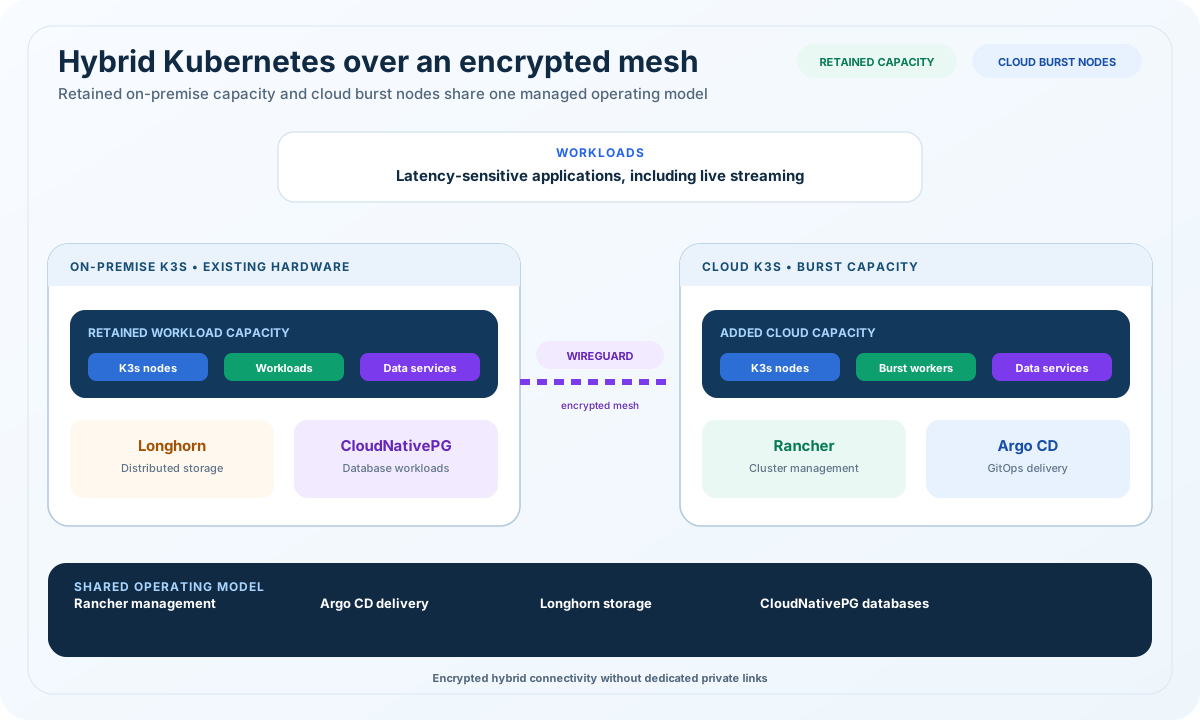
Hybrid K3s platform connecting retained on-premise capacity and cloud burst nodes through an encrypted WireGuard mesh with Rancher, ArgoCD, Longhorn, and CloudNativePG
AWS Advanced Tier Services PartnerAWS Advanced Tier Partner★ 4.9/5 on Clutch (9 reviews)Replies within 1 business day
Encrypted hybrid connectivityRetained on-premise capacityCloud burst capacity

The Challenge

A media company ran latency-sensitive streaming workloads on existing on-premise hardware. It wanted to add cloud burst capacity without throwing away that hardware.

It also did not want to pay for dedicated network links between sites, and the connection between on-premise and cloud had to be secure.

What We Built

Encrypted Mesh Between Sites

We connected every node with a WireGuard mesh, so workload traffic between on-premise and cloud is encrypted at the network layer without requiring dedicated private links.

One Kubernetes Platform Across Both

We ran K3s across on-premise servers and cloud nodes, managed through Rancher, so the existing hardware and added cloud capacity could operate through one platform model.

GitOps and Distributed Storage

We used ArgoCD for GitOps delivery, Longhorn for distributed storage, and CloudNativePG for databases, so state and deployments stay consistent across sites.

Retained On-Premise Capacity

We kept the client's existing hardware in active service for its latency-sensitive streaming workloads instead of requiring an immediate move to an all-cloud footprint.

Cloud Burst Capacity

We added cloud nodes for expansion while avoiding a dependency on dedicated private links between the on-premise and cloud environments.

The Result

  • The company retained its on-premise hardware as useful workload capacity rather than discarding the existing investment.
  • Cloud burst nodes added capacity through the same Kubernetes operating model.
  • WireGuard provided encrypted connectivity between the on-premise and cloud environments without requiring dedicated links.

Technology

K3sWireGuardRancherArgoCDLonghornCloudNativePG

Planning a similar platform?

Share the constraint behind your cloud, delivery, Kubernetes, or compliance project. We will confirm fit and identify three useful priorities for the first conversation.

Book an AWS review