CodetoKloudCodetoKloudBook an AWS review

AWS and Kubernetes Infrastructure for HIPAA-Regulated Workloads

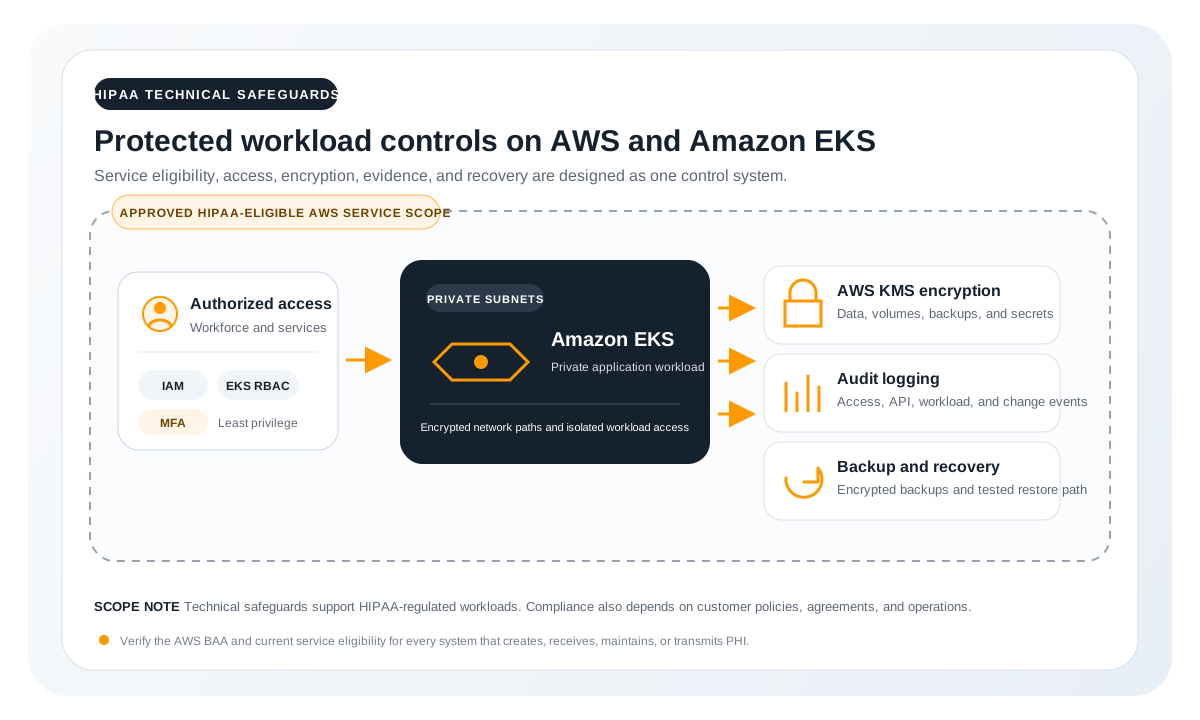
CodetoKloud helps healthcare organizations implement and document encryption, access controls, audit logging, private networking, backup, and recovery safeguards on AWS and Amazon EKS.

HIPAA-regulated AWS workload with private Amazon EKS, IAM, RBAC, MFA, KMS encryption, audit logging, and backup and recovery controls
AWS Advanced Tier Services PartnerAWS Advanced Tier Partner★ 4.9/5 on Clutch (9 reviews)Replies within 1 business day

Can AWS and Kubernetes support HIPAA-regulated workloads?

Yes. AWS offers a Business Associate Addendum (BAA) and a broad set of HIPAA-eligible services, and Kubernetes on Amazon EKS can host protected health information (PHI) when it is configured with the right controls. CodetoKloud implements encryption, access controls, audit logging, network isolation, backup, and recovery safeguards on AWS and EKS, then documents the technical environment for your internal compliance program and qualified advisors.

HIPAA compliance is an organizational responsibility that also includes policies, training, vendor management, and legal review. CodetoKloud focuses on the cloud and Kubernetes safeguards within the technical scope of that program.

Technical safeguards for HIPAA-regulated workloads

The technical safeguards that protect PHI on AWS and Amazon EKS.

HIPAA-Eligible Services & BAA

We architect workloads around HIPAA-eligible AWS services covered by the applicable AWS Business Associate Addendum (BAA), with an approved service boundary for protected health information (PHI).

Encryption of PHI

We encrypt PHI at rest with AWS KMS and in transit with TLS across every layer, databases, storage, container workloads, and backups, so sensitive health data is protected end to end.

Access Control (IAM & RBAC)

We enforce least-privilege access with AWS IAM, IAM Roles for Service Accounts, and Kubernetes RBAC, plus MFA and short-lived credentials, so only the right people and services can reach PHI.

Network Isolation

We run workloads in private, isolated VPCs and private Amazon EKS clusters with no public exposure, using security groups, network policies, and private endpoints to keep PHI off the public internet.

Audit Logging & Monitoring

We enable centralized audit logging (CloudTrail, CloudWatch) and continuous monitoring with Datadog and Prometheus, so every access to PHI is recorded and anomalies are caught early.

Backup & Disaster Recovery

We design encrypted backups and disaster recovery so PHI stays available and recoverable, a core HIPAA requirement, with tested restore procedures and defined recovery objectives.

Healthcare EKS implementation example

We migrated GoAgalia's healthcare workforce management platform to an Amazon EKS architecture designed for its HIPAA program, with private networking, autoscaling, GitOps delivery, and centralized observability.

~35% lower cloud cost850ms → 320ms API latency99.7% uptimeMTTR from 40+ min to 10-12 min
Read the GoAgalia case study →

Review the technical scope of your HIPAA program

Tell us about your healthcare workload. We will review the AWS or Kubernetes scope, confirm fit, and identify three technical priorities for the first conversation.

Book a HIPAA readiness review

HIPAA Compliance FAQs

Common questions about supporting HIPAA-regulated workloads on AWS and Amazon EKS.

Can AWS and Kubernetes support HIPAA-regulated workloads?

Yes. AWS offers a Business Associate Addendum (BAA) and HIPAA-eligible services, and Amazon EKS can host protected health information when the workload is configured and operated with the appropriate safeguards. CodetoKloud implements and documents encryption, access controls, audit logging, network isolation, backup, and recovery within the technical scope of your HIPAA program.

What technical safeguards do HIPAA-regulated workloads require?

The technical scope commonly includes encryption of PHI at rest and in transit, strict access controls, audit logging, network isolation, secure backups and recovery, and a BAA covering eligible services. HIPAA compliance also depends on organizational policies, training, vendor management, and legal review outside the infrastructure scope.

How does CodetoKloud secure protected health information (PHI) on AWS?

CodetoKloud secures PHI using AWS KMS encryption, private networking and isolated VPCs, least-privilege IAM and Kubernetes RBAC, encrypted secrets management, and continuous monitoring with tools like CloudWatch and Datadog. Only HIPAA-eligible AWS services are used for workloads that handle PHI.

Has CodetoKloud built infrastructure for HIPAA programs before?

Yes. CodetoKloud migrated GoAgalia's healthcare workforce management platform to an Amazon EKS architecture designed for its HIPAA program, with autoscaling, GitOps, and centralized observability. The engagement cut cloud costs by roughly 35%, reduced API latency from 850 ms to 320 ms, and reached 99.7% uptime.

How does the BAA work with AWS?

AWS provides a Business Associate Addendum that covers its HIPAA-eligible services. Your organization enters the applicable agreement with AWS. CodetoKloud helps define and implement an approved service boundary so PHI is processed and stored only through the services selected for that workload.

Can you help us prepare for a HIPAA assessment?

Yes. CodetoKloud implements and documents the technical safeguards a HIPAA assessment looks for, encryption, access control, logging, and disaster recovery. Formal assessments are performed by independent third parties; we prepare your infrastructure and evidence so that process goes smoothly.