An enterprise preparing for PCI DSS Level 1 needed developers to work inside controlled Google Cloud environments so cardholder-adjacent data would not be stored on local endpoints. We designed the technical foundation to support QSA review without claiming a certification outcome.
AWS Advanced Tier Partner★ 4.9/5 on Clutch (9 reviews)Replies within 1 business dayThe organization needed consistent developer workspaces inside a controlled cloud boundary rather than relying on varied local environments for work near cardholder data.
The design also had to document how workstation, network, encryption, logging, and access controls mapped to PCI DSS responsibilities before QSA pre-assessment and review.
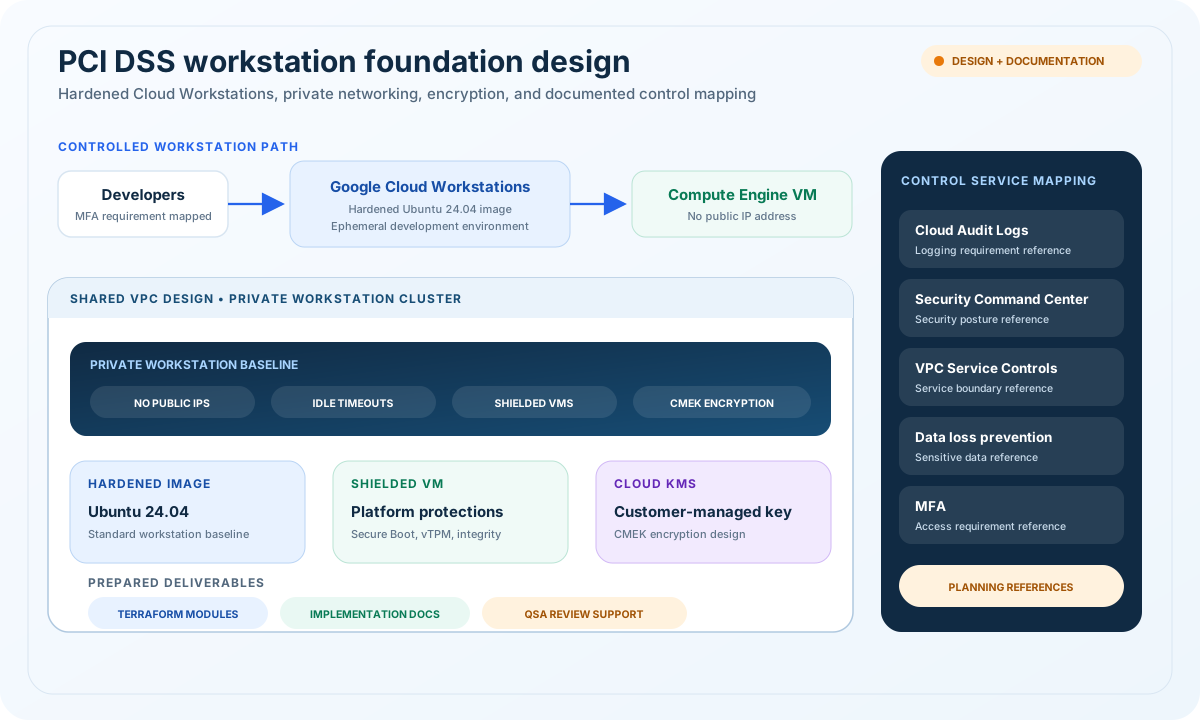
We built custom Ubuntu 24.04 workstation images on Google's base image, removed unnecessary packages, added auditd, AIDE, and ClamAV, disabled USB storage, and moved repeatable setup into the image build.
We designed Cloud Workstations without public IP addresses and added Shielded VMs with Secure Boot, virtual TPM, and integrity monitoring. Cloud KMS customer-managed encryption keys and idle timeouts added further data and session controls.
We recommended and documented a Shared VPC model for the multi-team environment, including its boundaries and tradeoffs compared with isolated VPCs and peering.
We delivered Terraform modules alongside console-path documentation and mapped relevant controls to Google Cloud services such as Cloud Audit Logs, Security Command Center, VPC Service Controls, DLP, and MFA enforcement.
We documented an implementation sequence through QSA pre-assessment and review, anchored the design to Google's PCI responsibility matrix, and made clear which responsibilities remained with the organization.
Share the constraint behind your cloud, delivery, Kubernetes, or compliance project. We will confirm fit and identify three useful priorities for the first conversation.
Book an AWS review