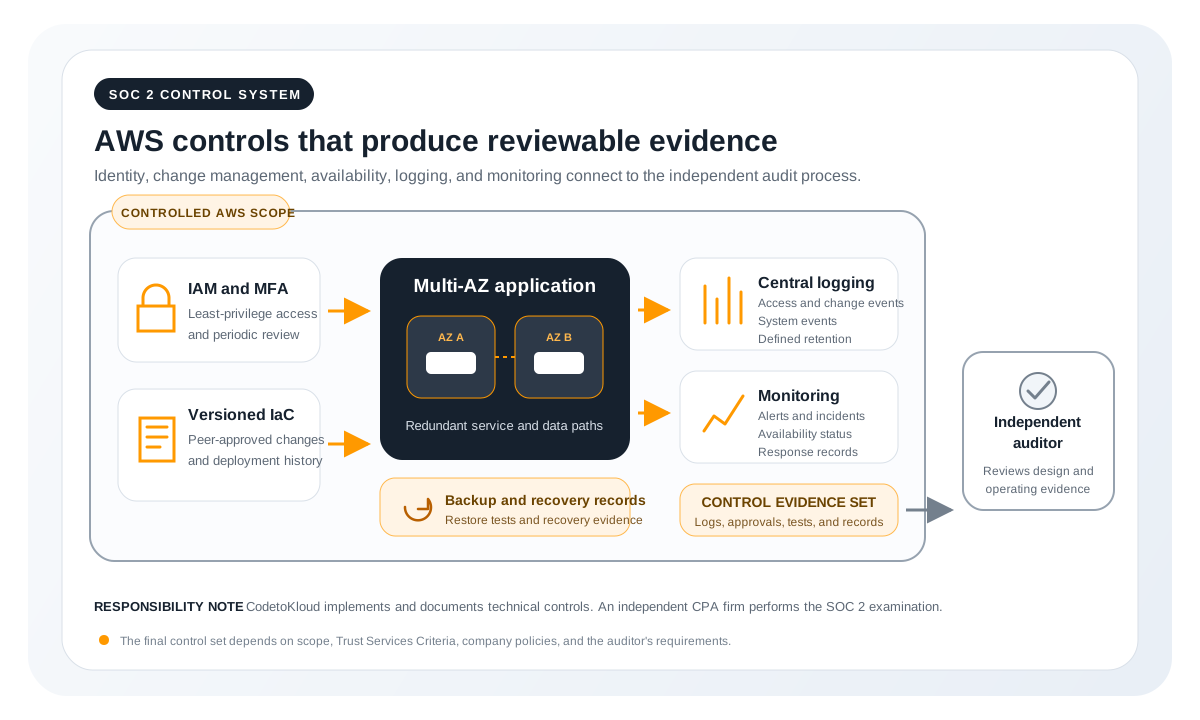
CodetoKloud helps teams assess AWS control gaps, implement access, logging, change, monitoring, and recovery controls, and organize technical evidence for an independent SOC 2 auditor.
AWS Advanced Tier Partner★ 4.9/5 on Clutch (9 reviews)Replies within 1 business daySOC 2 readiness connects the Trust Services Criteria selected for your program to controls your team can operate and demonstrate. CodetoKloud reviews the AWS environment, closes agreed technical gaps, and documents evidence for identity, change management, logging, availability, encryption, and incident response.
Only an independent CPA firm can issue a SOC 2 report. Your organization remains responsible for policies and operating the controls. CodetoKloud supports the AWS infrastructure and technical evidence within the agreed scope.
Mapped to the Trust Services Criteria your auditor evaluates.
Least-privilege IAM, role-based access, MFA, and short-lived credentials so only authorized identities reach production systems and data.
Centralized, tamper-evident logging with CloudTrail and CloudWatch, so every meaningful action is recorded and available as audit evidence.
Infrastructure-as-code with Terraform and Git-based review, giving you versioned, approved, auditable changes, exactly what SOC 2 change management expects.
Continuous monitoring with Prometheus, Grafana, Datadog, and CloudWatch, with alerting on availability and security events mapped to the Trust Services Criteria.
Encryption at rest with AWS KMS and in transit with TLS across databases, storage, and workloads to protect confidential data.
Documented incident response and disaster recovery processes so security and availability events are detected, contained, and recovered from predictably.
Share your audit window and current AWS concerns. We will confirm fit within one business day and use a focused 30-minute review to identify three practical technical priorities.
Book a SOC 2 readiness reviewPassed audit with 99.99% uptime.
Common questions about getting SOC 2 audit-ready on AWS.
SOC 2 is a security framework based on the Trust Services Criteria, security, availability, processing integrity, confidentiality, and privacy. A SOC 2 report is issued by an independent auditor after evaluating your controls. CodetoKloud builds and operates the AWS infrastructure and controls that a SOC 2 audit evaluates.
No vendor can issue your SOC 2 report. An independent CPA firm evaluates the controls and issues the report. CodetoKloud assesses and remediates agreed AWS infrastructure gaps, implements technical controls, and organizes evidence for your auditor. Your organization remains responsible for policies and operating the controls.
CodetoKloud implements least-privilege IAM and access controls, centralized audit logging, change management through infrastructure-as-code, encryption at rest and in transit, monitoring and alerting, and incident response processes, mapped to the SOC 2 Trust Services Criteria.
It depends on the current state of your infrastructure. CodetoKloud starts with a gap assessment, then closes the technical gaps, often the fastest path is standardizing infrastructure-as-code, logging, and access controls before your audit window begins.
Yes. CodetoKloud provides the technical documentation, architecture diagrams, and control evidence your auditor needs, and remediates findings on the infrastructure side so your audit stays on track.
Compare focused compliance services and choose the next step for your AWS environment.